How to assign the right user permissions
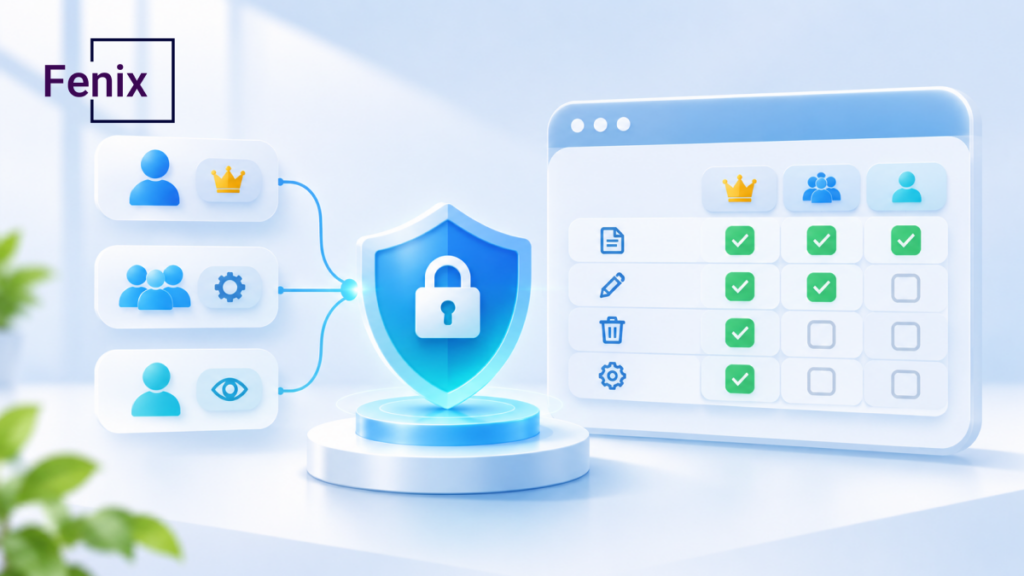
An employee exporting the entire customer list may indicate excessive access. Too little access also causes problems: staff cannot open assigned records or requests stall when a manager is away. Permissions should enable assigned work while blocking unauthorized actions.
Login and authorization are different. Login establishes identity; authorization decides which data and actions that identity may access. This article uses a hypothetical expense process with claimants, managers and accounting. The business must confirm its own policy rather than adopt the example unchanged.
1. Define users, actions and data scope
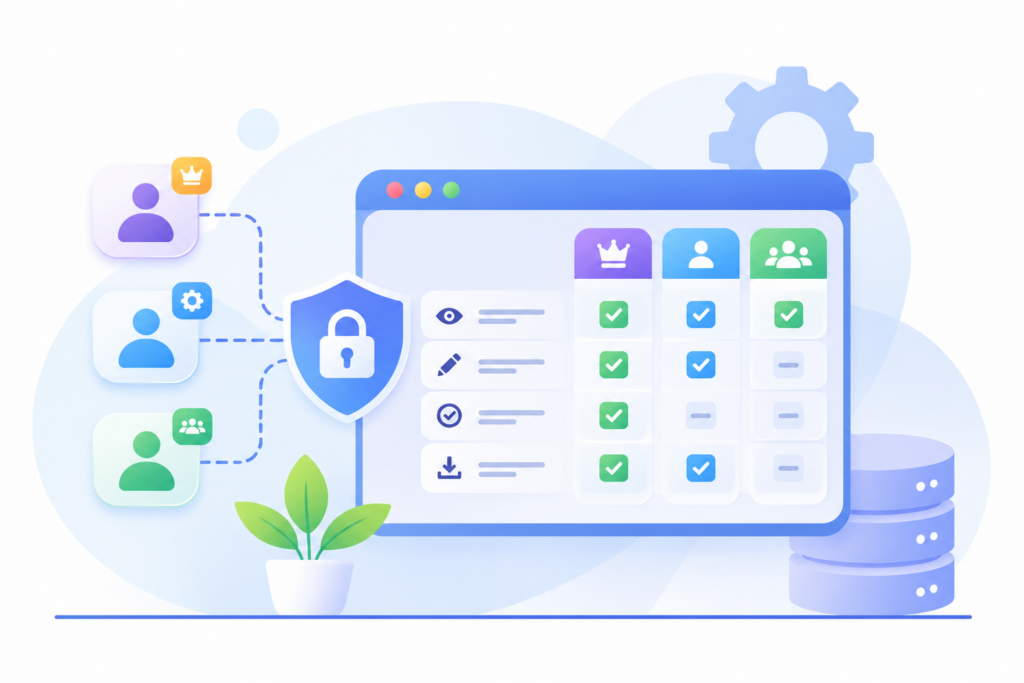
Start with explicit actions: view, create, edit, submit, approve, delete or export. Labels such as employee or team leader leave too much unclear. A manager may approve assigned cases without viewing all company records; accounting may need amounts without full personnel information.
Then define scope: own records, team, branch or company-wide. In the example, claimants view their claims, managers their assigned approvals and accounting its allotted scope. Record limits such as no self-approval where the business adopts that policy.
Separate related permissions. Viewing a record does not automatically allow every attachment download or a bulk export for offline use. Ask why exports are needed and who needs them. Do not broaden access merely because it is the quickest support workaround.
Describe these boundaries as scenarios with an approving owner, so developers do not invent company policy. What Is Requirements Analysis? A First Step Toward Clearer Development explains how to turn business needs into testable requirements.
A permission might say: accounting can view and record payment for approved claims in its assigned unit, but cannot change the payee after payment. This combines role, action, data and condition. It is an example to confirm, not a ready-made financial rule.
2. Define access as a record changes status
A claimant may edit a draft but not directly alter an approved or paid claim. Permissions must account for status and the next step. For returned records, define what may change, who resubmits and how the approver sees the changes.
For confirmed data, use an agreed correction route such as returning or recording an adjustment with history. Do not solve it by giving everyone administrative access. Preserve the previous result and identify who may approve changes so decisions remain traceable.
3. Plan for delegation and staff changes
Delegation during absence needs a scope and duration, not shared manager credentials. Specify eligible claims, self-approval limits and expiry. Records should distinguish the person acting from the person who delegated authority.
For transfers or departures, review old access and unfinished work together. Reassign pending records and address personally owned reports or integrations. Removing an account without transferring work can stop a process; transferring work while retaining old access leaves unnecessary permissions.
Combining roles should not automatically combine every permission and bypass limits. In a small business with overlapping duties, agree suitable review or alternative approval arrangements. The software must reflect that decision rather than apply a generic role template.
When operators change, transfer permissions alongside responsibilities and open work. How to hand over software to the next team helps verify actual takeover capability rather than receipt of an account list.
Urgent access still needs approval and review. For temporary incident access, record purpose, scope and the person checking its removal. Convenience should not silently turn a temporary permission into permanent access.
4. Test boundaries and keep permissions current
Test allowed and denied actions with representative accounts. Users should access assigned records but not out-of-scope ones, including through direct links. A hidden button does not establish that underlying access paths are controlled.
Retest status changes, delegation expiry and staff transfers. Check reports, notifications and attachments for unintended disclosure too. Use authorized scope and suitable data, not arbitrary access to other people’s real records.
Include these cases in acceptance and process-change checks. Software acceptance: What should your business test? helps prepare data, expected results and reports for boundaries that fail.
After launch, assign approval for new access and an appropriate review schedule. Logs help trace actors and changes but do not establish that a decision was authorized. Start with a real process and its roles when discussing permissions with Fenix.
If staff repeatedly ask others to act for them, review the workflow and permissions. Scope may be wrong or an alternative route unclear. Business and technical owners should agree the fix and retest both allowed and denied actions, avoiding a new risk as a workaround.